A managed services provider (MSP) that adds penetration testing to its catalog is adding a line with real margin and a real audit deadline behind it. This guide is about the economics of that line: where pentesting fits in a modern MSP catalog, how the MSP and MSSP models differ, how to package and price a resold pentest, and what changes when the partner behind it is channel-only. MSP Pentesting sells only through MSPs, MSSPs, vCISOs and GRC firms, so we have a view on this and we'll say what it is. If you're still choosing the vendor, that's a separate job: how to vet penetration testing providers covers it.
What Is a Managed Services Provider?
Think of a managed services provider like a personal trainer for your IT systems. A trainer doesn't just show up after you pull a muscle. They build a long-term plan to improve your strength and prevent injuries. An MSP does the same for your technology, focusing on proactive care instead of just fixing problems.
This is different from the old "break-fix" model, where you'd only call an IT person after a server crashed. That approach is expensive and guarantees downtime. An MSP partnership gives you predictable costs and constant oversight, making sure your systems are always optimized and secure.
The MSP Shift From IT Maintenance to IT Security
The role of an MSP has changed a lot. With cyber threats on the rise, security isn't just an add-on service anymore. It's at the core of what a managed services provider does. MSPs are on the front lines, helping businesses defend against attackers and meet tough compliance standards like SOC 2, HIPAA, and PCI DSS.
This security-first mindset is essential. An MSP’s job has grown from keeping systems running to building a digital fortress around your clients' data. This makes advanced security services, like a penetration test, a critical part of their offering. This move to outsourced IT management isn't a small trend; it's a huge industry shift.
The numbers tell the story. The market is projected to soar, driven by demands for cloud, cybersecurity, and AI integration. For any MSP, vCISO, or IT reseller, this growth is a massive opportunity to deliver the security solutions your clients need, like a comprehensive penetration testing engagement.
Traditional IT vs Managed Services Provider (MSP)
The old way was all about reacting to problems. The MSP model is built on preventing them from ever happening.
The value of an MSP isn't just in fixing computers. It's in providing the stability and security that lets a business focus on growth, not on IT fires.
Core Services Every Modern MSP Should Offer
A modern managed services provider does more than just fix computers. Clients now expect a true technology partner who can handle everything from daily IT needs to sophisticated security threats. This means your service catalog needs to be both broad and deep.
The foundation starts with infrastructure and cloud management. This includes managing servers, networks, and user devices to make sure they're always patched and running smoothly. It also means guiding clients through cloud migrations and managing those environments to control costs. Think of it as keeping the digital engine of your client's business perfectly tuned.
Alongside that, data backup and recovery are non-negotiable. It’s not a question of if a client will face data loss, but when. A great MSP provides automated, tested backups and has a clear disaster recovery plan ready to go. This gets clients back online fast and cuts down on expensive downtime.
Why MSP Security Services are So Important
Cybersecurity isn't just another service; it's the glue holding everything together. For any managed services provider today, security has to be part of everything you do. Your clients face constant threats and look to you as their first line of defense. This is your biggest opportunity to deliver massive value.
This protection starts with getting the essential security layers right. This includes endpoint protection to defend devices from malware, firewall management to block unwanted traffic, and vulnerability management to patch weaknesses before attackers find them. This is where you prove your value as a true partner.
Once you have those foundational security measures locked down, the next step is to test them. This is where advanced security assessments come in. Offering services like a manual penetration test shows you're serious about protecting clients from determined attackers, not just automated bots. A pen test, also known as penetration testing, is like hiring ethical hackers to find security holes before real criminals do. It validates your security work and is often required for compliance frameworks like SOC 2 and ISO 27001.
For MSPs, vCISOs, and GRC companies, providing pentesting elevates your role from an IT provider to a security partner. It proves that you don't just build the walls; you prove they'll hold up under attack. This proactive approach to risk assessment is what separates a good MSP from a great one.
Understanding the MSP Versus MSSP Distinction
It’s easy to mix up the acronyms, but knowing the difference between a Managed Services Provider (MSP) and a Managed Security Services Provider (MSSP) is key. Think of an MSP as your IT general practitioner. They handle your overall tech health, from network performance to data backups.
An MSSP is a specialist, the heart surgeon for your cybersecurity. Their entire world is detecting and neutralizing threats. They often run a 24/7 Security Operations Center (SOC) and use advanced tools that are too complex and expensive for a typical MSP to manage alone.
While an MSP handles a broad range of IT functions, an MSSP brings a specific set of tools and a specialized mindset. Their services are focused on defense, compliance, and active threat hunting. This diagram breaks down the core services you’d expect from a modern MSP, with cybersecurity at the center.
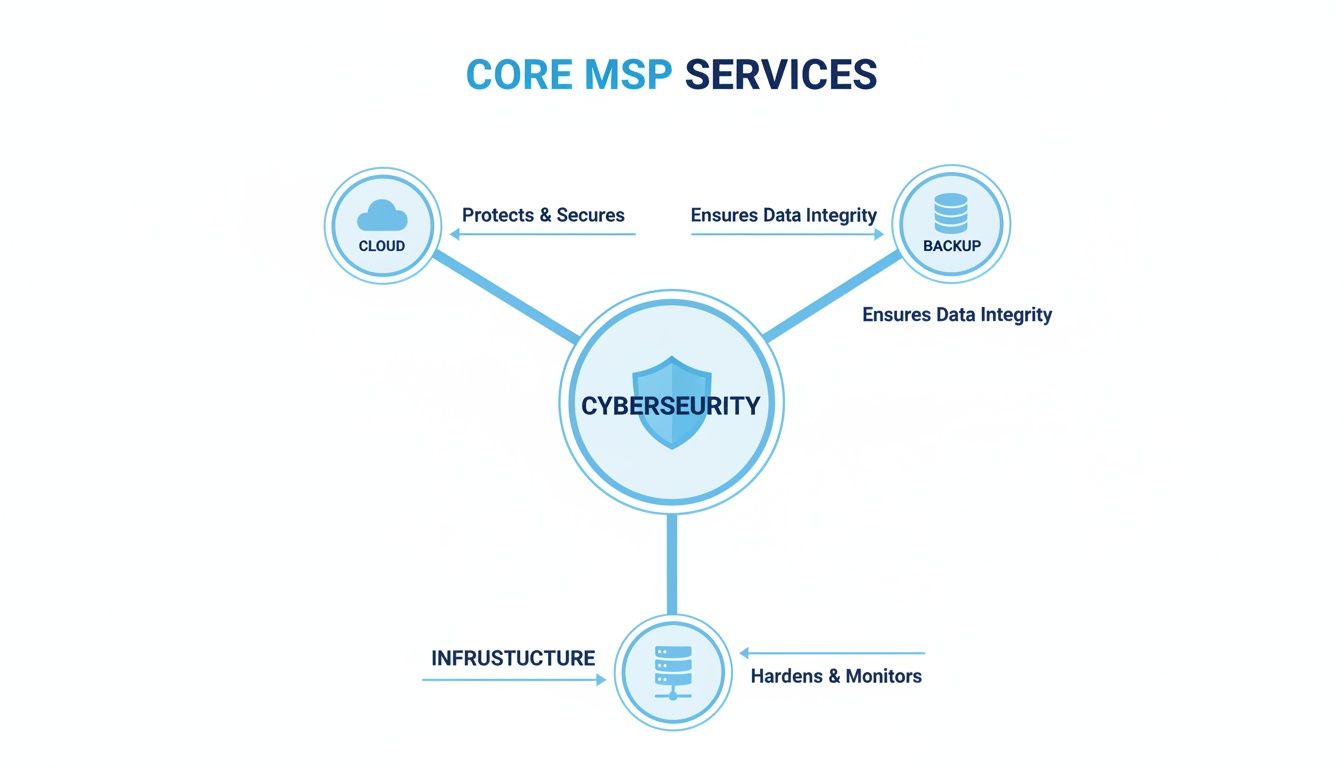
While infrastructure, cloud, and backup are key pillars, cybersecurity is the thread that connects them all. It’s the most critical piece of an MSP’s entire offering.
The main difference is that MSPs focus on keeping the lights on, while MSSPs watch for anything trying to turn them off. You can get a deeper look into what a security-first provider offers by exploring the world of MSSP security services. This distinction matters because clients increasingly demand specialized security.
For an MSP, building a full MSSP operation is a massive undertaking. The smart answer is partnership. By working with a channel-only security provider, an MSP can deliver highly specialized services like a manual penetration test under their own brand. A true partner never competes with you for your clients. We provide the certified pentesters (holding OSCP, CEH, and CREST) so you can focus on your core business. You get to offer affordable, fast, and effective white label pentesting that helps your clients achieve compliance.
Why Cybersecurity Is Your Biggest MSP Opportunity
Cybersecurity isn't just another service. It's the biggest growth engine for any modern managed services provider. Your clients are hearing about data breaches and feeling pressure to meet compliance rules like SOC 2, HIPAA, and PCI DSS. This is a huge problem that your MSP is perfectly positioned to solve.
This is your chance to turn security into a high-margin, recurring revenue stream. When you add services like manual pentesting, you're proving your value and building incredible trust with your clients. This gives you a serious competitive advantage in a crowded field. Every headline about a ransomware attack is an opportunity for you.
By offering a complete security stack, you transform your relationship. You're no longer just the "IT guy." You become an essential partner in their business success. The numbers don't lie. The managed services boom is fueled by cybersecurity. You can dig into more of the data by exploring these key MSP market statistics.
Compliance isn't optional anymore. Frameworks like ISO 27001 and SOC 2 often require a penetration test to prove security controls work. For any client in a regulated industry, a pen test is a mandatory part of their risk assessment. This gives you a clear reason to offer penetration testing. For MSPs focusing on robust defense, implementing comprehensive Data Security Best Practices is crucial.
You don't have to build an in-house pentesting team. By partnering with a 100% channel-only provider, you can offer white label pentesting under your own brand. Our certified OSCP, CEH, and CREST experts deliver fast, affordable, and thorough manual pentesting that you can resell. We only exist to help you succeed.
How to White Label Penetration Testing Services
Offering a penetration test is a great way to boost revenue, but building an in-house team is tough. You have to find and retain expensive, certified talent. White label pentesting is the smart shortcut, letting you resell expert security services under your own brand without the huge overhead. It's like a craft brewery using a co-packer to bottle their beer. You put your label on a premium product while a partner handles the complex work.
This model lets you instantly add high-demand services to your catalog. You can offer everything from web app pentesting to internal network assessments. This makes you fully equipped to help clients meet demanding compliance frameworks like SOC 2 and HIPAA. This makes you a much more valuable partner.
The economics work like any other resold service, with two differences. First, you buy at a partner rate and sell at your own price, so the margin is whatever the gap is, and a fixed partner price list matters more than a low headline number because it lets you quote without a call. Second, the deliverable carries your name, which means the report quality is your reputation and the retest policy is your renewal. If the partner includes remediation retesting, bundle it into your price rather than listing it as a line item; the client sees a complete service and you keep the margin up front. The arithmetic, including how to set the client price against your partner rate, is worked through in reseller pricing math for MSP pentesting.
Packaging follows the client's audit calendar. A one-off compliance test suits a client with a SOC 2 or PCI DSS date in front of them. An annual bundle (external and internal network testing plus a web application test, with the retest included) fits a client who has to show evidence every year. A premium tier adds quarterly application testing or continuous validation on top. Every package should state scope, cadence, report delivery and retest window in writing, because those four things are what the client's auditor asks about. The mechanics of the white-label arrangement itself are in our guide to how white label pentests get delivered, and the broader market context is in the MSP Alliance's view of the managed services market.
Choosing the Partner Is a Separate Job
The margin model above only holds if the partner behind it doesn't become your competitor. That's a contract question before it's a price question: whether the vendor sells to end clients at all, what the non-solicit says, who owns the relationship in the report. We keep the selection criteria in two places so this guide can stay about the economics. The full scorecard, from tester credentials to auditor fit to retest policy, is in how to vet penetration testing providers. The contract clauses that decide whether you still hold the account in three years are in how to vet a pentest vendor's channel terms.
Our answer to those questions is the white-label pentest partner program: channel-only, a 24-month non-solicit in every reseller agreement, testers holding OSCP, CREST and CEH, the report under your brand, and the retest included on a timeline scoped to the engagement.
Frequently Asked Questions About MSP Pentesting
When MSPs, vCISOs, and GRC companies start thinking about adding penetration testing to their services, a few common questions always come up. Here are the straight answers you need to make the right call for your business.
The smartest and fastest way for a managed services provider to offer a pen test is through a white label reseller program. Building an in-house team of ethical hackers is a massive undertaking. A white-label approach lets you partner with a channel-only provider that does the actual pentesting, and you deliver the report under your own brand.
How much margin should an MSP expect on a resold pentest? It depends on the gap between your partner rate and your client price, and on whether the retest and the report rewrites are included or billed separately. Fixed partner pricing you can quote from, a retest that's included, and no rush fees are what keep the margin predictable. Which partner to choose is a different question, and we answer it separately in the provider vetting guide.
What’s the difference between a pen test and a vulnerability scan? Think of a vulnerability scan as an automated camera that flags a door that might be unlocked. It's useful but shallow. A penetration test is when a security expert tries to pick that lock and see what they can do once inside. A pen testing engagement is a manual, goal-driven attack simulation that shows you the real-world risk.
At MSP Pentesting, we're here to make our partners the go-to security advisors for their clients. As a 100% channel-only provider, we deliver fast, affordable, and expert manual pentesting services that you can sell as your own. Ready to add a serious security offering to your MSP? See how we support reseller partners.